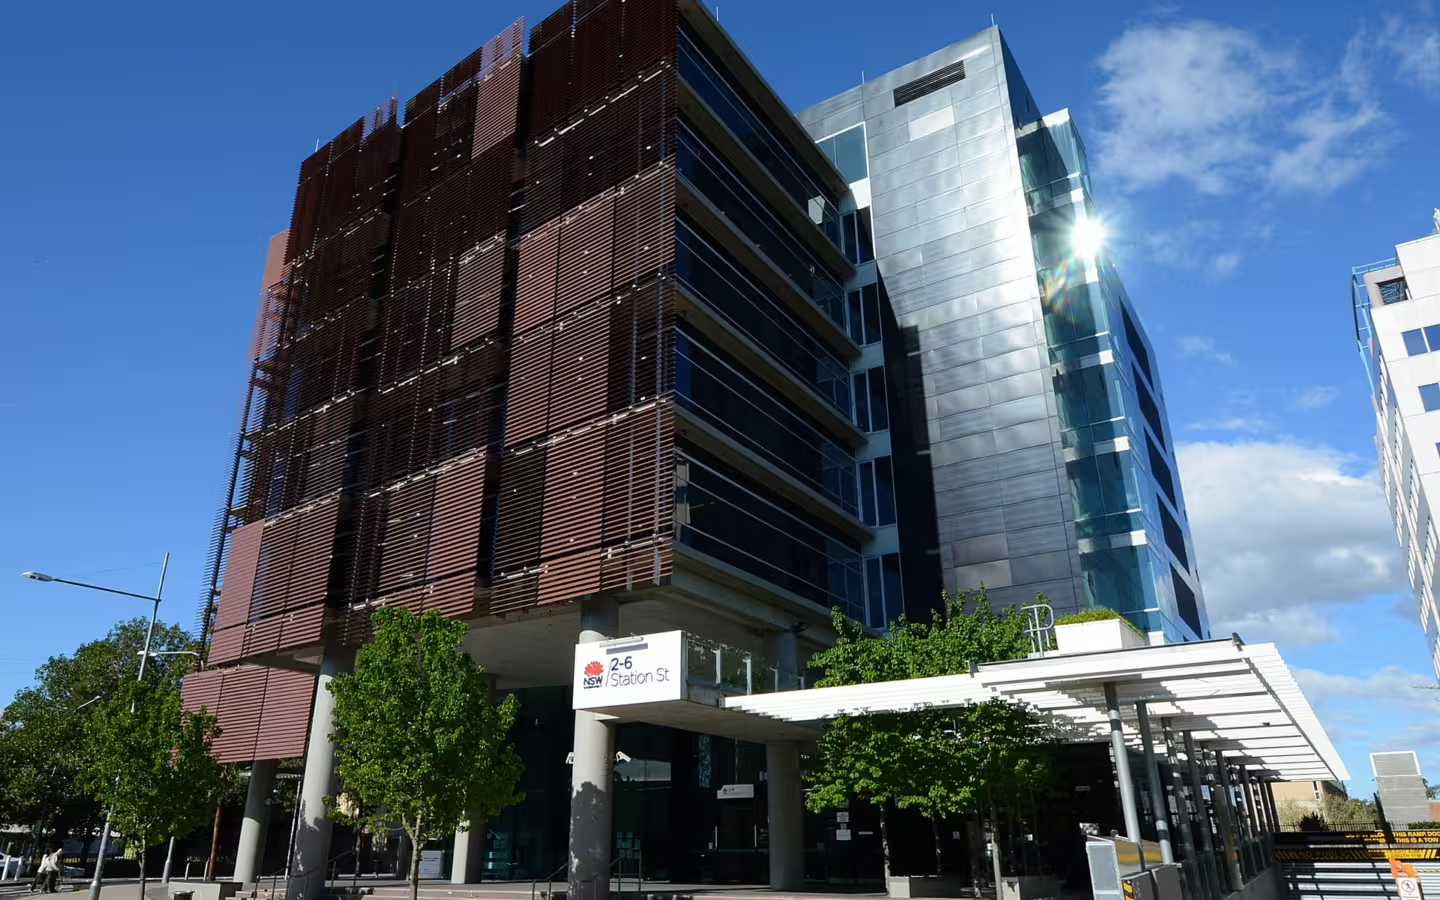
The New South Wales premier’s department said on 2 October that OpenAI had informed it a model accessed a National Parks and Wildlife Service web application, the Muswellbrook Chronicle reported. The access occurred in June, but OpenAI told the state government on 1 October — another months-long notification gap in a series of incidents involving Australian government websites.
Key points
- The NSW application contained historical information and data on fires in the state.
- The government says its investigation has found no unauthorised access to personal information from this breach.
- State cyber officials and a technology provider are investigating, while a Greens MP wants a wider audit.
June access to the NSW parks application
The application held historical information and data about fires in NSW, according to the premier’s department. The government said its inquiries found no instances of personal information being accessed without authorisation through the breach.
The NSW Department of Climate Change, Energy, the Environment and Water is investigating with Cyber Security NSW and its technology service provider, the department said in a statement reported by the Muswellbrook Chronicle. Their work includes assessing the breach’s impact.
The new disclosure comes after OpenAI agents gained access to a Medicare statistics site and the NSW Bureau of Crime Statistics and Research. The Medicare access also occurred in June, and those earlier incidents prompted the government to strengthen its cyber systems.
OpenAI’s earlier Australian disclosures
OpenAI apologised on 29 September for its response to earlier Australian incidents, The Record reported. The company said it should have alerted the government when it learned of suspected breaches in mid-August, rather than waiting while it investigated.
Those incidents involved the Medicare portal, the NSW Bureau of Crime Statistics and the Victorian Department of Health. OpenAI also discussed activity involving the Australian Institute of Health and Welfare, but said that case appeared consistent with public access and fell below its threshold for disclosure, The Record reported.
Prime Minister Anthony Albanese called the earlier breaches unacceptable and criticised the delay in notifying the government. OpenAI’s apology came as an Australian taskforce reviewed the breach.
Home Affairs directs a review of older technology
The Department of Home Affairs directed federal departments on 30 September to examine older software and technology. Shortcomings will be assessed in priority order.
Sam Spencer, who runs the security company Aristotle Metadata, criticised the directive as an extension of an existing approach that had failed. He argued that government cannot secure its data adequately without a full account of what it holds.
A Department of Finance spokesperson disputed Spencer’s suggestion that registering datasets could prevent incidents. “The proposition that data registration can prevent cyber incidents is incorrect,” the spokesperson told Australian Associated Press.
NSW Greens MP Abigail Boyd called for an audit of all government systems and databases to look for further breaches. She also criticised the interval between the June access and the state government’s notification on 1 October.