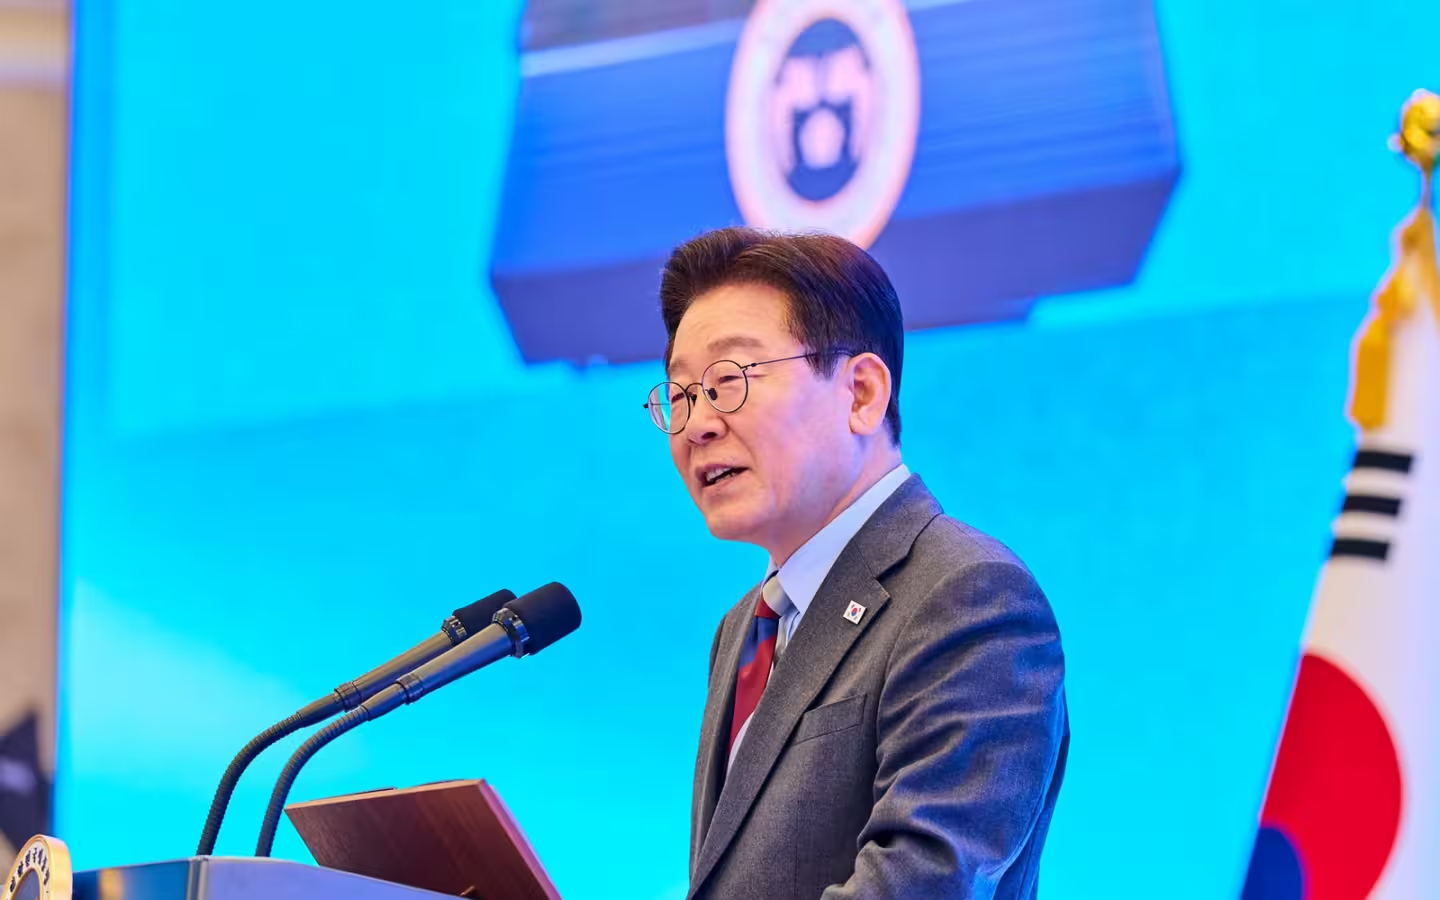
South Korean President Lee Jae Myung called for a thorough investigation into hacking attacks at banks and other financial institutions on 4 October, Anadolu Agency reported. The order covers a series of customer-data leaks, while the country’s financial regulator has not ruled out the use of AI tools in the attacks.
Key points
- Lee ordered an investigation into attacks affecting banks and other financial institutions.
- Shinhan Bank said personal information belonging to about 25,000 customers was leaked.
- Accounts differ on whether AI tools were used in the Shinhan attack.
- Financial authorities have ordered security checks beyond the affected firms.
Lee’s 4 October investigation order
Presidential spokesperson Kang Yu-jung said Lee instructed authorities to investigate the attacks and develop measures to address them, Anadolu Agency reported. The affected institutions include major banks as well as other financial firms.
Financial Services Commission chairman Lee Eog-weon and Financial Supervisory Service governor Lee Chan-jin met with heads of affected firms. Lee Eog-weon said security breaches had been detected across commercial banks, savings banks and specialised credit finance firms within a short period.
Lee Eog-weon said information that could be used for unauthorised payments did not appear to have been compromised. He warned that leaked details could still be used for voice phishing or other scams, and did not rule out AI tools being used in the attacks.
Shinhan Bank and the AI question
Shinhan Bank said personal information belonging to about 25,000 customers had leaked, including names, phone numbers and annual incomes. An external attacker accessed a loan-broker service, Startup Fortune reported.
Anadolu Agency reported that hackers used advanced AI tools in the Shinhan attack, an account it attributed to Yonhap sources. Startup Fortune reported a narrower finding: on infrastructure thought to be linked to recent attacks, researchers detected signs of a Chinese-language, open-source AI penetration-testing tool. It said the tool’s use in the Shinhan breach has not been confirmed.
Lee Eog-weon called for banks to develop defences that use AI against AI-driven threats, according to Startup Fortune. His call comes as financial authorities examine security across the sector, rather than only at firms that have reported breaches.
Yegaram’s 40,000 customers and wider checks
Yegaram Savings Bank said hackers took names, birth dates and contact details belonging to about 40,000 customers. Intruders continued to target six services, including a mobile loan-status page, after the bank blocked an initial IP address.
KB Kookmin Bank and Hana Bank reported breaches affecting 119 and 89 customers respectively. The incidents have involved externally exposed loan and business-support systems outside the banks’ core deposit and transfer infrastructure.
Financial authorities have ordered computer-system checks at banks and card companies beyond those already affected. Lee Eog-weon’s emergency meeting included the heads of Shinhan, Kookmin, Hana and Busan banks, Hyundai Capital, and Yegaram and Welcome savings banks.